Introduction
According to IDC research, 78% of business-use smartphone shipments worldwide are Android. Android is clearly the world’s most popular Operating System. Due to its diversity of platform, flexibility of form factor and economic reasons, Android has become the go-to OS for many Enterprises world-wide. Also, since Android is open-source, it has become the choice of platform for OEM’s producing mobile devices for the mass market.
What is Android Enterprise?
Android Enterprise is an initiative led by Google to allow the use of Android devices and apps in the workplace. It provides robust management APIs that helps EMM solutions to confidently deploy and manage Android devices for enterprise use.
Evolution of Android Enterprise
EMM (Enterprise Mobility Management) solutions depend on APIs to communicate with and control managed devices.
In 2010, with Android version 2.2, Google introduced Device Management capabilities with Device Admin (DA) API’s. The DA API’s had a lot of limitations in terms of usability and security. It also failed to keep up with the requirements and new challenges that emerged from the workforce.
In 2014, Google introduced a new set of device management APIs with Android Lollipop (5.0). This introduced two management modes-
Fully Managed (Device Owner) – Company Owned (COD) device use-cases
Work Profile (Profile Owner) – Bring Your Own Device (BYOD) use-case
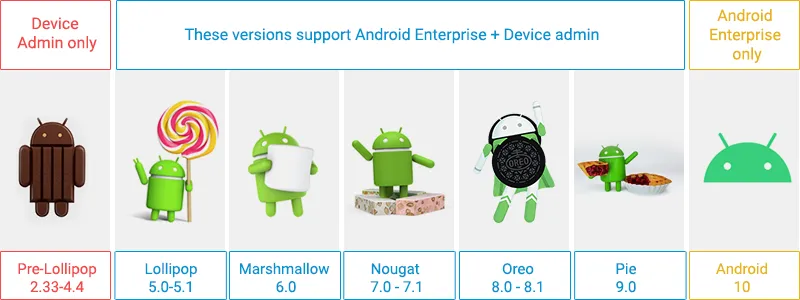
In August 2018, Google released Android 9 (Pie) in which several functionalities of the Device Admin (DA) API’s were deprecated by Google.
In September 2019, Google released Android 10 in which Device Admin (DA) API’s are completely deprecated. Devices from Android 2.x to 4.x – Only Device Admin API support
Devices from Android 5.x to 9.x – Both Device Admin API and Android Enterprise API support
Devices from Android 10 – Only Android Enterprise API
Company Owned vs Employee Owned device:
Employee Owned:
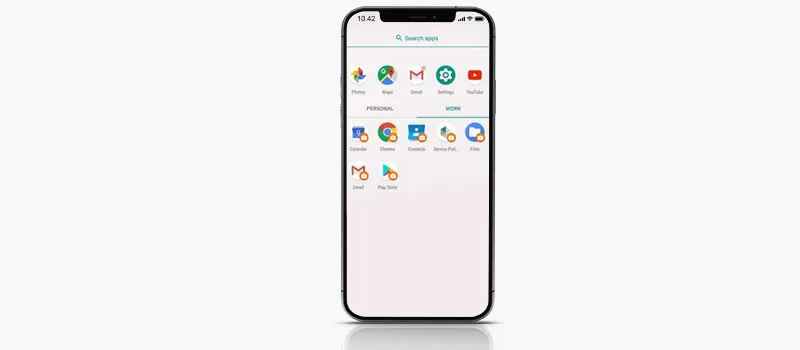
These devices are owned by the employee. Employees can bring their own devices to work and use them for office purposes. Work profiles are the suggested deployment method for BYOD devices. It separates work apps from personal apps. Work apps are labelled with a briefcase icon.
Company Owned Devices:
Company Owned Device is fully owned and managed by an employee’s organization. These are dedicated for work purpose
Provisioning Methods:
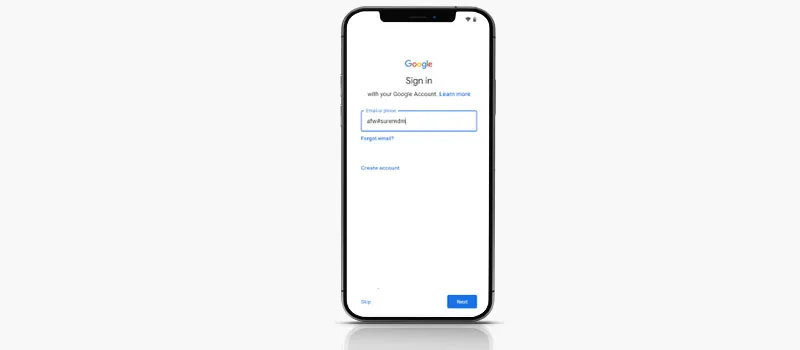
Using DPC identifier
Enter afw#<EMMCode> on Google sign-in page on initial device setup to start the provisioning process. Available on Android 6.0+
QR Code
Tap 6 times on the welcome screen post factory reset to get QR code scanner. Scan QR Code to start the provisioning process. This requires an out-of-box device or factory reset for an existing device. This is available on Android 7.0+ devices
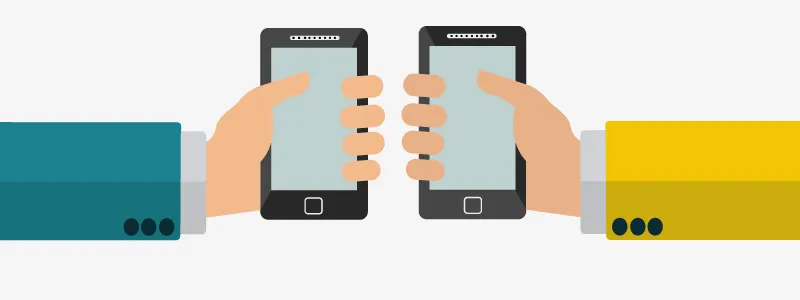
NFC Bump
Bump against NFC on the initial screen post device boot up to start device provisioning process. This requires an out-of-box device or factory reset for an existing device. This is available on Android 5.1+ devices
Zero Touch Enrollment (ZTE)
For this enrollment method, the device needs to be purchased directly from an enterprise reseller or Google partner. Fresh out-of-box devices will get the profile configured in the ZTE portal after startup. This is available on Android 7.0+ (for Pixel only) or 8.0+ (Compatible device) or any device running Android 9.0+
What is Android Enterprise Recommended?
Android Enterprise Recommended is an initiative led by Google for devices, vendors and partners to make it easy for enterprises to select, deploy and manage Android devices.
Android Enterprise recommended devices are Google recommended list of devices that satisfied the minimum requirements set by Google. Detailed requirements can be found here
Android Enterprise recommended complete device list can be found here
Android Enterprise recommended complete EMM list can be found here
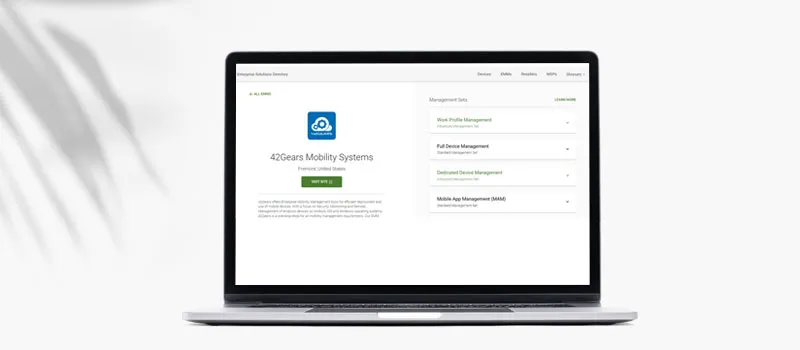
Image showing 42Gears EMM solution as Android Enterprise Recommended EMM solution
Get started with Android Enterprise:
Getting started with Android Enterprise typically involves the below steps:
Sourcing Android devices – Select an Android device based on your needs and budget. You can always refer to the Android Enterprise recommended devices list.
Choosing EMM solution – Choose an EMM solution that facilitates all your organization requirements
Deploy devices -Set up and deploy devices using the provisioning method that best suits your use case.
Benefits of Android Enterprise
Below are few benefits:
Easy provisioning of devices – Reduces time and manual effort
Work Profile support – Personal devices can be used for office use without compromising data security
Secure App distribution – Distribute apps through Managed Google Play – Play for work
Enterprise security features – Enforce security policies related to apps, networks and content
Choose Best device, Best EMM solution for your needs using Android Enterprise recommended
OEM config – OEM’s can provide additional API’s on top of Android Enterprise and can be managed easily through EMM
Conclusion:
Android Enterprise is empowering organizations to have granular control over the devices used for work purposes, thereby enhancing employee productivity and data security. With the depreciation of Device Admin APIs by Google, it is imperative that Android Enterprise is the future for Enterprise Android device Management.